If you've spent any time in web security, you've heard of the OWASP Top 10. It's the closest thing our industry has to a shared vocabulary for what actually breaks websites. Updated periodically by the Open Web Application Security Project, it ranks the most common and damaging vulnerabilities found in real applications, based on data from thousands of organizations.
Knowing the list is one thing. Doing something about it is another. This is where a web application firewall earns its keep. Let's walk through each major OWASP category and look at how a web application firewall actually helps, and where it doesn't.
What the OWASP Top 10 Actually Measures
The OWASP Top 10 isn't a checklist someone dreamed up in a meeting. It's built from real-world vulnerability data, contributed by security firms, bug bounty programs, and application testing tools. Every few years, the list shifts based on what's actually being exploited in the wild.
The current categories cover things like broken access control, cryptographic failures, injection flaws, insecure design, and security misconfiguration. Some of these are code-level problems that only a developer can fix. Others are exactly the kind of thing a web application firewall is built to catch at the network edge, before a malicious request ever reaches your application.
Injection Attacks: SQL Injection and Command Injection
Injection flaws happen when untrusted input gets passed into a query or command without proper handling. A classic SQL injection attempt might look like appending ' OR '1'='1 to a login field, hoping to bypass authentication entirely.
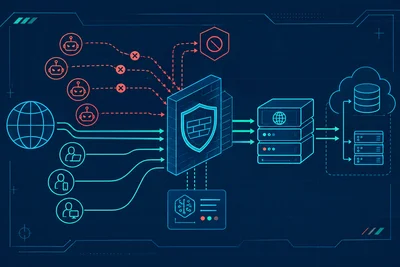
A web application firewall inspects incoming requests for these known attack patterns. It recognizes suspicious characters, malformed queries, and command syntax that has no business showing up in a form field. When it spots one, it blocks the request before it reaches your database layer.
This doesn't replace parameterized queries in your code. But it does add a second line of defense for the vulnerabilities your developers haven't found yet, or the third-party plugin nobody's audited in two years.
Broken Access Control
This category covers situations where users can access data or functionality they shouldn't. Think of someone changing a URL parameter to view another customer's invoice, or bypassing role checks to reach an admin panel.
A web application firewall has limits here. It can enforce rate limiting and block obvious path traversal attempts, and some setups let you restrict access to sensitive URLs by IP or geography. But access control logic ultimately lives in your application. This is one area where the firewall supports your defenses rather than replacing them.
Where Rules Fill the Gap
Rule-based filtering can catch attempts to reach known admin paths, block direct access to configuration files, and flag unusual request patterns like a single IP hitting hundreds of different account endpoints in a minute. That behavior pattern alone is often enough to stop credential stuffing before it does damage.
Cryptographic Failures
This one is mostly about what happens before a request even reaches your firewall. Weak TLS configurations, expired certificates, and unencrypted data in transit fall outside what a web application firewall inspects.
That said, a proper hosting setup handles this layer separately. Automatic certificate renewal and modern TLS configurations close most of the gaps here, so the firewall can focus on what happens after the connection is secured. If you're curious how certificate management works day to day, we cover that in more detail on our SSL overview.
Cross-Site Scripting (XSS)
XSS attacks inject malicious scripts into pages viewed by other users, often through comment fields, search boxes, or URL parameters. The script runs in the victim's browser and can steal session cookies or redirect users to phishing pages.
A web application firewall is genuinely strong here. It scans incoming and sometimes outgoing content for script tags, encoded payloads, and known XSS signatures. Because these patterns are well documented, detection rates tend to be high, and false positives are manageable when the rules are tuned properly.
Security Misconfiguration
Default admin passwords, exposed debug endpoints, directory listing left enabled. These mistakes are common and easy to exploit once found. A web application firewall can hide some of the symptoms by blocking access to known sensitive paths, but the real fix is closing the misconfiguration itself.
This is why layered protection matters more than any single tool. We wrote about this idea in Why Layered Website Security Protection Beats Any Single Tool Every Time, and it applies directly here. The firewall buys you time and reduces exposure while the underlying issue gets fixed.
Vulnerable and Outdated Components
Outdated plugins, libraries, and frameworks are one of the most common entry points for attackers, especially on WordPress sites running abandoned plugins. A web application firewall can block known exploit signatures targeting specific CVEs, which buys valuable time between a vulnerability being disclosed and a patch being applied.
This is especially relevant if you're running WordPress. We go into more depth on the login and plugin side of things in Why WordPress Security Best Practices Start With Your Hosting Environment, Not Your Plugins.
Server-Side Request Forgery (SSRF)
SSRF tricks a server into making requests to internal systems it shouldn't be able to reach, often used to access cloud metadata endpoints or internal APIs. Modern web application firewall rulesets increasingly include SSRF-specific detection, watching for suspicious outbound request patterns and blocked internal IP ranges in user-supplied URLs.
Building Rules That Actually Work
A web application firewall is only as good as its rule set. Overly aggressive rules block legitimate traffic and frustrate real users. Overly permissive rules let attacks slip through. Good implementations use a mix of:
- Signature-based rules for known attack patterns
- Behavioral analysis to catch anomalies signatures miss
- Regularly updated rule sets that track new CVEs
- Custom rules tuned to your specific application
We covered the mechanics of this in more detail in WAF Rules Explained: How Your Web Application Firewall Decides What to Block, if you want to go deeper on the rule logic itself.
Where This Leaves You
The OWASP Top 10 is a map of what attackers actually do, not a theoretical exercise. A web application firewall covers a meaningful chunk of that map, particularly injection attacks, XSS, and known exploit signatures. It's weaker against logic flaws like broken access control, which need to be fixed in your application code.
If you're evaluating hosting, ask directly whether a web application firewall is included and actively maintained, not just installed once and forgotten. Managed hosting that keeps rule sets current, including ours, takes this off your plate entirely so you're not the one tracking new CVEs every week. You can see how this fits into a broader server security setup on our WAF overview page.
The real takeaway: treat the OWASP Top 10 as your baseline, not your ceiling. A good firewall handles the repetitive, well-known attack patterns so your team can focus on the harder problems that live in your own code.