Web ApplicationFirewall
Our WAF inspects every request and blocks malicious traffic before it reaches your website - automatically and in real time.
What is a WAF?
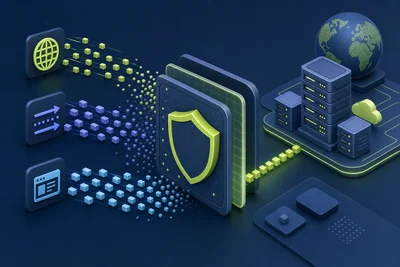
A Web Application Firewall sits between your visitors and your website, analyzing every HTTP request. It blocks SQL injection, cross-site scripting, file inclusion attacks, and other common threats listed in the OWASP Top 10.
Unlike network firewalls that operate at lower layers, a WAF understands application-level protocols. This allows it to make intelligent decisions about which requests are legitimate and which are malicious - without disrupting real visitors.
Protection Features
Rules Engine
Custom rules for known IPs, countries, bots, URIs, query parameters and request patterns, with rate limiting when you need it. Set them for a single website, or server-wide on a managed VPS.
OWASP Rules
Industry-standard ruleset protecting against the OWASP Top 10 vulnerabilities.
Custom Rules
Create your own rules to match specific traffic patterns or block known threats.
XML-RPC Protection
Block or limit XML-RPC requests that are commonly exploited in brute-force attacks.
Proxy Blocking
Detect and block requests from known proxy networks and anonymizers.
Real-time Analytics
Monitor blocked requests, rule triggers, and traffic patterns in real time. One-click AI analysis by Proper.
Protection Modes
Balanced
RecommendedBlocks known threats with smart bypasses for safe paths. Ideal for most websites.
- Injection, XSS and file-upload attempts blocked
- Known admin paths and safe URL parameters skip the checks
- OWASP rules enabled
- Log only mode available to test before enforcing
Strict
Full blocking without safe-path bypasses. Stricter but may need tuning.
- The same attack blocking as Balanced
- Safe-path bypasses disabled
- Every request is checked in full
- May need tuning for complex apps
Advanced
Set the two allowlists yourself instead of taking a preset.
- Each allowlist switched on or off by hand
- Log only mode available while you test
- OWASP rule set tuned by hand in the panel
- Switch back to a preset at any time
How It Works
Request Arrives
A visitor or bot sends an HTTP request to your website.
Rules Engine
Your own rules are checked here: block or allow by address, country, path or request pattern, and known safe paths are let through.
OWASP Inspection
Requests pass through industry-standard rules for deep inspection.
Clean requests reach your site. Threats are blocked instantly.
WAF Protection is Standard
Every plan includes our Web Application Firewall - no add-ons, no extra charges.
View Plans