Every day, your website gets visitors you never see in your analytics dashboard. Bots scanning for vulnerable plugins. Scripts trying default admin passwords. Automated tools probing your contact form for a way to inject malicious code. Your regular traffic reports won't show you any of this. Your web application firewall logs will.
If you've never looked at your WAF logs, you're missing one of the most useful threat intelligence sources you already have access to. Let's talk about what's actually in there and how to read it.
What a Web Application Firewall Actually Logs
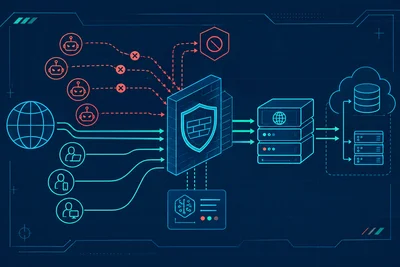
A web application firewall sits between incoming requests and your website, inspecting each one before it reaches your application. When a request looks suspicious, like a SQL injection attempt or a request trying to access a file it shouldn't, the firewall blocks it and records the details.
A typical log entry includes:
- The source IP address making the request
- The URL or endpoint being targeted
- The rule that triggered the block (SQL injection pattern, XSS attempt, path traversal, etc.)
- The timestamp
- The HTTP method and headers, including the user agent string
- The country the request originated from
On its own, one log entry doesn't tell you much. But look at hundreds or thousands of them over time, and patterns start to emerge.
Reading the Patterns: Who Is Actually Attacking You
Automated Scanners vs. Targeted Attackers
Most of what shows up in your web application firewall logs isn't a human sitting at a keyboard. It's automated scanning. These bots crawl huge ranges of IP addresses looking for known vulnerabilities, like an outdated plugin or an exposed configuration file. You'll recognize this pattern by its shape: short, repetitive bursts hitting the same handful of URLs (/wp-admin, /.env, /phpmyadmin) from IPs that disappear after a few requests.
A targeted attack looks different. You'll see a single source, or a small cluster of related IPs, probing multiple different attack vectors against the same page over a longer period. That's a sign someone is specifically interested in your site, not just sweeping the internet for easy targets.
Geographic Patterns
If you don't do business internationally, request volume from countries outside your customer base is worth watching. A spike in malicious requests from a specific region, especially one with no legitimate reason to be visiting your site, often points to a coordinated scanning campaign rather than random noise.
Repeat Offenders
Some IP addresses show up again and again across weeks or months. These are often part of larger botnets or come from hosting providers known for hosting command-and-control infrastructure. Keeping a running list of these addresses, and checking them against reputation databases, helps you decide which ones are worth blocking outright at the firewall or server level rather than just filtering their requests.
What to Actually Do With This Information
Reading logs is only useful if it changes what you do. Here's where the information pays off:
- Tighten rules where you see repeated attempts. If your logs show constant SQL injection attempts against a specific form, that's a signal to double check input validation on that exact form, not just rely on the firewall to catch everything forever.
- Block at the network level when it makes sense. Persistent attackers from a single IP or narrow range are good candidates for a server-level block, which stops the traffic before it even reaches the application layer. For this, server firewall controls for blocking specific IPs work well alongside your WAF rules.
- Watch for false positives. Sometimes legitimate users or integrations get caught in overly aggressive rules. Reviewing logs regularly helps you catch this before it costs you real traffic or broken functionality. We've gone into this in more depth in False Positives in a Web Application Firewall and How to Tune Them.
- Correlate with other signals. Cross-reference WAF logs with your uptime and server monitoring to see if blocked traffic spikes line up with performance dips. That correlation often reveals application-layer DDoS attempts disguised as normal traffic.
Why This Matters More Than It Seems
Understanding who's targeting your site isn't just an academic exercise. It shapes real decisions: which countries to restrict if you're seeing abuse with no legitimate traffic from them, which endpoints need extra validation, and whether your current rule set is actually keeping up with what's hitting your server.
This connects to the broader OWASP Top 10 framework that most web application firewalls are built around; if you want a refresher on what those common threats look like, we covered them in OWASP Top 10 Threats and How a Web Application Firewall Addresses Each One.
Making Log Review Sustainable
Nobody has time to manually scroll through thousands of log lines every day. The practical approach is to set up regular summaries, weekly or monthly, rather than trying to review everything in real time. Look for new patterns, recurring IPs, and any noticeable shift in attack type. A managed host should be doing this kind of review on your behalf as part of keeping the web application firewall rules current. On our own servers, we treat this as an ongoing process rather than a one-time setup, since attack patterns shift constantly and rules that worked last month might miss something new this month.
If you're trying to decide whether your current setup gives you this kind of visibility at all, that's worth checking directly with your host. You can read more about how this kind of protection works in our WAF overview.
The Takeaway
Your WAF logs are a direct window into who's trying to get into your site and how. Most site owners never look at them, which means they're missing free threat intelligence that's already being collected. Start by checking your logs once a week. Look for repeat IPs, unusual geographic spikes, and which specific pages get targeted most. That alone will tell you more about your actual risk than any generic security checklist.