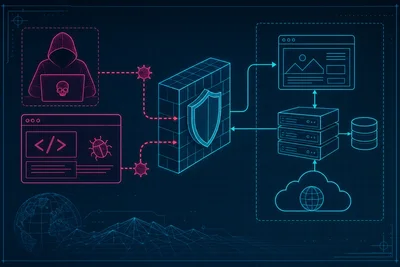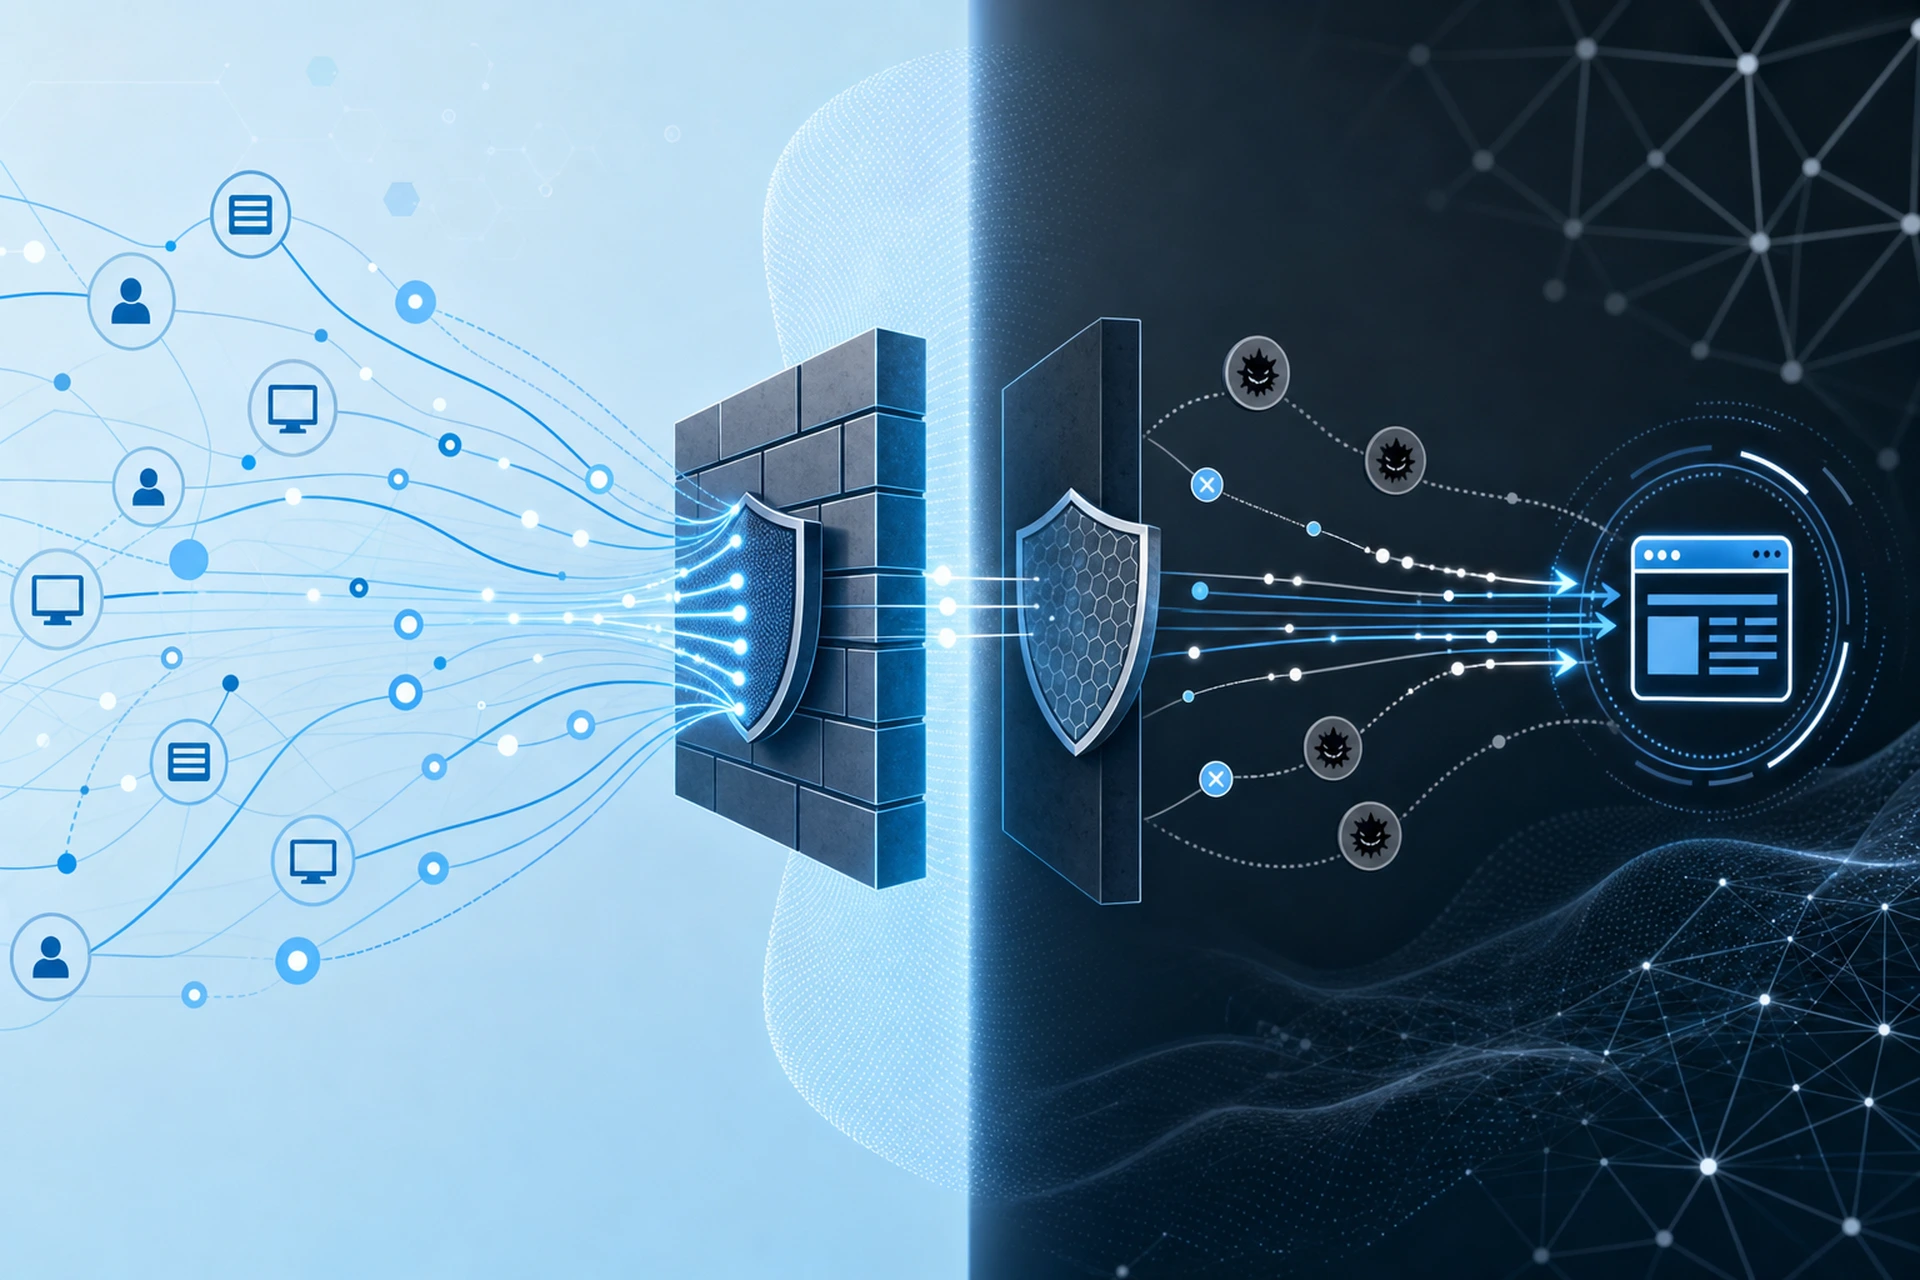
If you've ever asked your hosting provider or IT person "don't we already have a firewall?" when someone suggests adding a web application firewall, you're not alone. It's one of the most common points of confusion in website security. Both tools are called firewalls, both block bad traffic, and both sound like the same thing on paper. They're not.
Understanding the difference matters because relying on the wrong one leaves a real gap in your defenses. Let's break down what each one actually does, in plain terms.
What a Network Firewall Actually Does
A network firewall works at the infrastructure level. Think of it as a bouncer standing at the front door of your server, checking IDs before anyone gets inside the building at all.
It looks at things like:
- Which IP addresses are trying to connect
- Which ports they're trying to reach (like port 22 for SSH or port 3306 for MySQL)
- What protocol they're using (TCP, UDP, ICMP)
- Whether the connection pattern looks like a scan or a flood
A network firewall doesn't know or care what's inside an HTTP request. It doesn't read the URL, the form data, or the cookies. It just decides: should this connection be allowed to reach this port on this server, yes or no?
This makes it excellent at blocking things like unauthorized access attempts to your database port, random port scans from bots hunting for open services, or traffic from IP ranges you've explicitly blocked. If you've ever blocked an IP or closed off a port on a server, that's network firewall territory.
Where the Network Firewall Falls Short
Here's the catch. Your website needs port 443 (HTTPS) open to the public. Everyone needs to reach it, that's the whole point of having a website. A network firewall can't close that port without taking your site offline, which means it can't stop attacks that come through the front door disguised as normal web traffic.
An attacker sending a malicious SQL injection string through your contact form is using port 443, just like every legitimate visitor. To a network firewall, that traffic looks completely fine. It arrived on the right port, using the right protocol. The firewall has no way to know the request itself is dangerous, because it never looks that closely.
What a Web Application Firewall Does Differently
This is where a web application firewall picks up the job. Instead of stopping at "is this connection allowed," a web application firewall reads the actual content of the request. It inspects the URL parameters, form fields, headers, and cookies, and compares them against known attack patterns.
A web application firewall can catch things like:
- SQL injection attempts hidden in a login form
- Cross-site scripting payloads tucked into a comment field
- Suspicious file upload attempts trying to plant malicious scripts
- Requests that don't match expected patterns for your specific application
We covered how these rules actually get built and enforced in WAF Rules Explained: How Your Web Application Firewall Decides What to Block. The short version: a web application firewall operates at layer 7, the application layer, which is exactly where a network firewall stops paying attention.
Why You Need Both, Not One or the Other
Neither tool replaces the other. They protect different layers of the same stack.
Think of your infrastructure like a building. The network firewall is the security guard checking who's allowed in the front entrance. The web application firewall is the person watching what visitors actually do once they're inside, making sure nobody's trying to pick a lock on the server room or slip something into a filing cabinet they shouldn't touch.
A site with only a network firewall is exposed to the entire OWASP Top 10 category of application attacks, things like injection flaws and cross-site scripting, because none of that traffic ever gets flagged as suspicious at the network level. We go through those specific threats in more depth in OWASP Top 10 Threats and How a Web Application Firewall Addresses Each One.
On the flip side, a site with only a web application firewall and no network-level protection is still exposed to port scanning, brute-force login attempts against exposed services, and certain types of denial-of-service traffic that never even reach the application layer.
How This Plays Out in Real Hosting Environments
On a managed VPS, both layers usually live side by side without you needing to configure either one manually. The server firewall handles which ports are reachable and from where. Separately, request filtering at the application layer inspects the actual HTTP traffic hitting your site, checking things like request patterns, country of origin, and rate limits before anything reaches your code. That's the setup we run here, so a request has to pass both checks before it ever touches your application.
If you're managing your own server and only have one of these two layers in place, it's worth checking what your current setup actually covers. A lot of site owners assume "firewall" is a single checkbox, when really it's two separate jobs. You can read more about how request filtering and country-based rules work on our WAF overview, and how port and IP-level rules are handled on the firewall page.
A Quick Way to Check What You Have
Ask yourself these two questions:
- Can I block a specific IP address or close a specific port on my server? That's your network firewall doing its job.
- Does anything inspect the actual content of form submissions, URLs, or headers for attack patterns? That's your web application firewall, or the lack of one.
If you can only answer yes to the first question, you have half the protection most modern websites actually need.
The Takeaway
A network firewall and a web application firewall aren't competing tools, they're teammates working two different layers of the same problem. One decides who gets to knock on the door. The other reads what's written on the note they're handing you once they're inside. Skipping either one means leaving a door unguarded, even if you didn't realize it was open.