If you've ever sent an important email and had it arrive 15 minutes later than expected, greylisting might be the reason. It's one of the oldest tricks in email spam prevention, and it still works surprisingly well. But like most spam-fighting tools, it has a cost. Let's look at how it actually works and when it turns into a headache.
What Is Greylisting?
Greylisting is a simple idea based on how spam gets sent. Most spam comes from botnets and throwaway scripts that fire off a message once and never try again. Real mail servers, on the other hand, are built to retry.
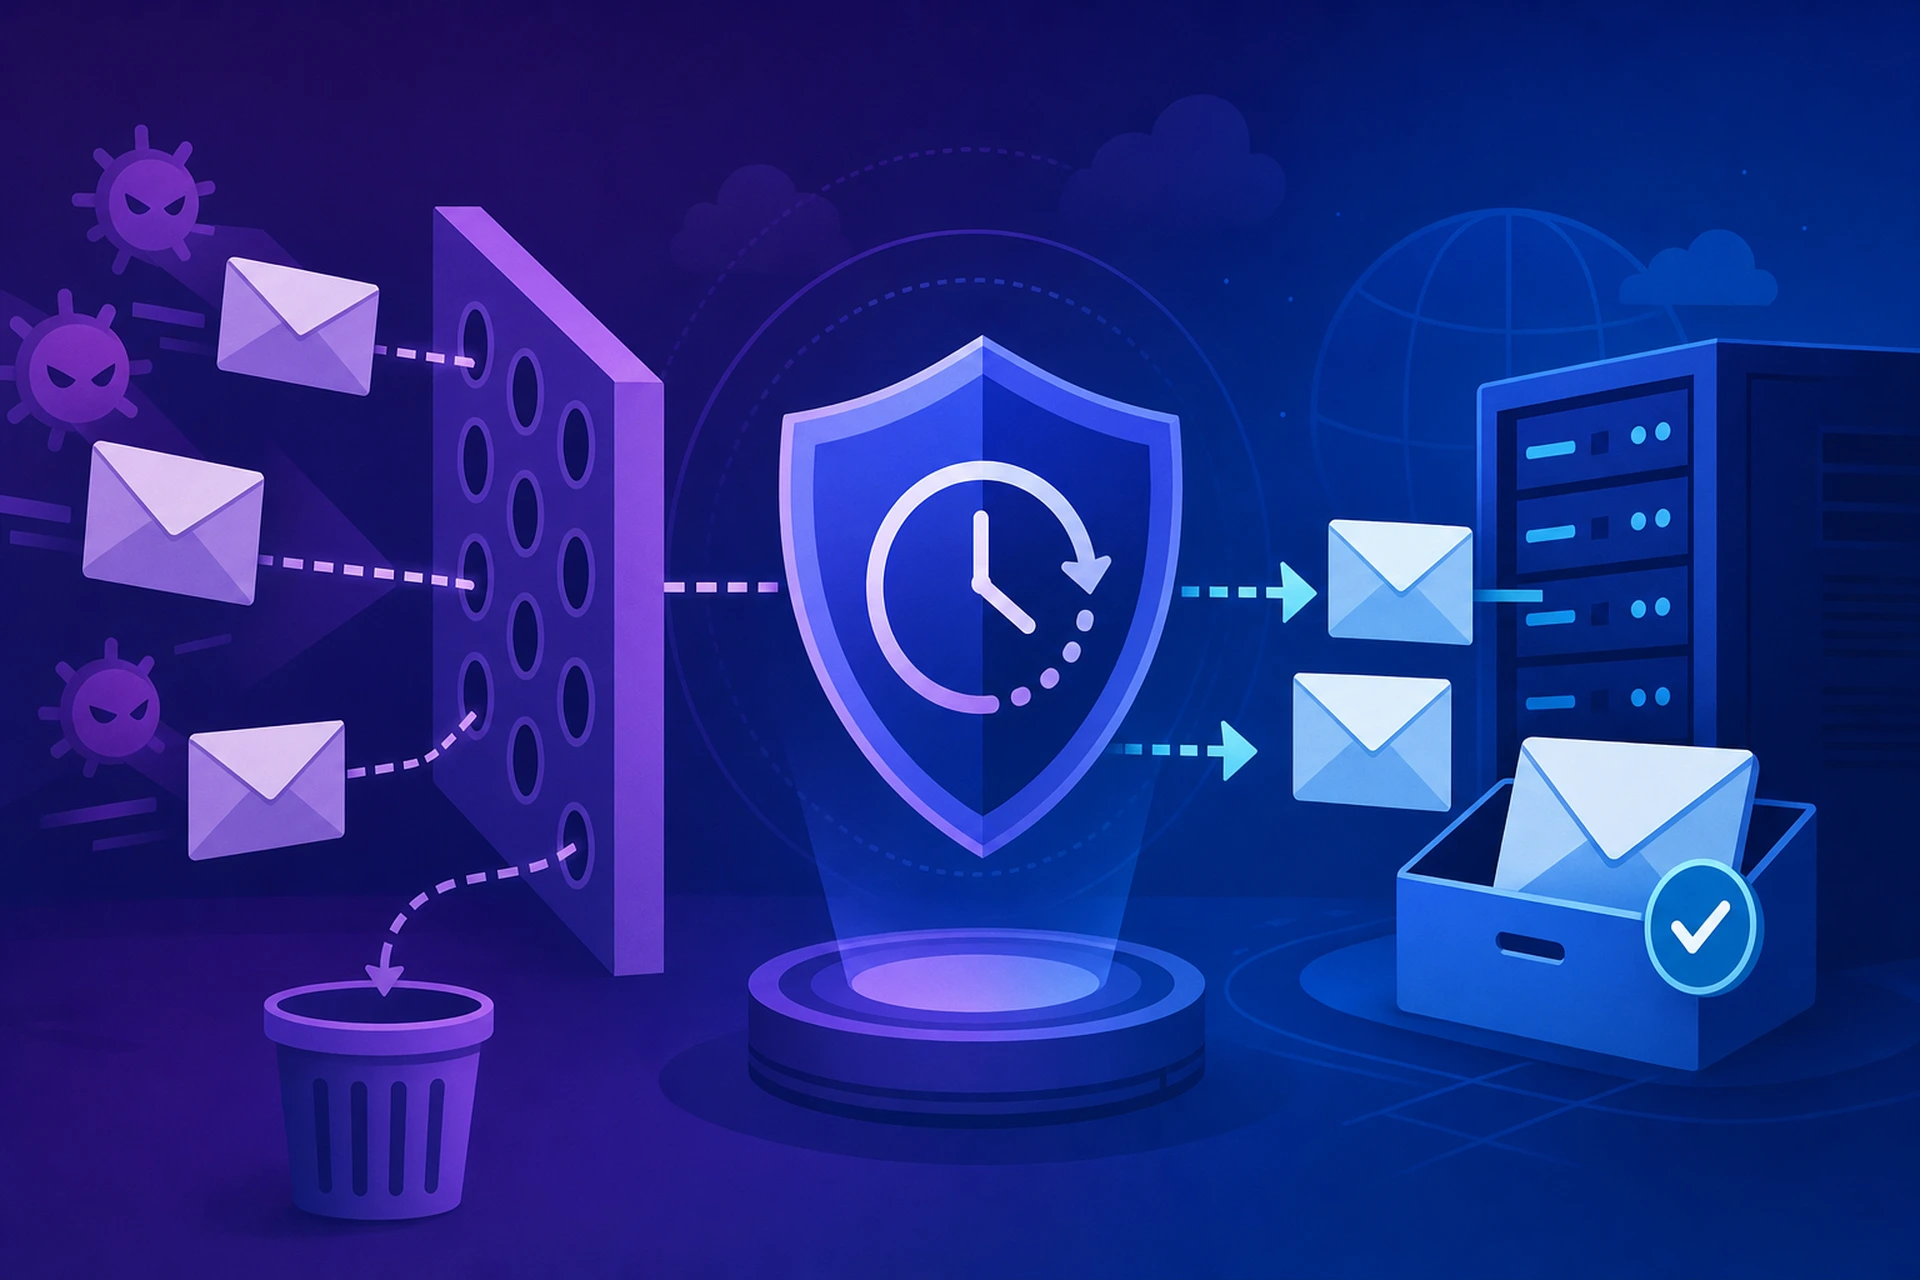
Here's the trick: when an unfamiliar server tries to deliver an email to your inbox for the first time, your mail server temporarily rejects it with a soft error, something like "try again later." A legitimate sending server sees that response and, following standard email protocol, waits a few minutes and tries again. Spam software usually doesn't bother. It moves on to the next target.
If the second delivery attempt comes in after a set waiting period (often somewhere between 1 and 15 minutes), the message gets accepted and the sender's address gets whitelisted for future mail. That's the entire mechanism. No content scanning, no keyword matching, just a waiting game that spammers usually fail.
Why Greylisting Works So Well
The beauty of greylisting is that it stops spam before it even reaches more resource-intensive filters. You're not analyzing message content or checking blocklists. You're just making the sender prove it behaves like a real mail server.
This makes greylisting cheap to run and effective against a huge chunk of low-effort spam operations. Studies over the years have shown it can block a large percentage of spam attempts outright, since so many spam senders skip retries entirely to maximize their sending volume.
It also pairs well with other layers of defense. We've covered how sender reputation works and how it forms the foundation of deliverability, and greylisting fits neatly alongside reputation checks, content filters, and authentication records like SPF and DKIM.
When Greylisting Causes Real Problems
Here's where things get tricky. That delay isn't always harmless.
Delayed delivery for time-sensitive email
Password reset links, two-factor authentication codes, order confirmations. All of these depend on speed. If a legitimate sender's server has an unusual retry schedule, a greylisted message might sit in limbo for much longer than a few minutes. Some servers only retry every 30 minutes, or even longer.
Load-balanced sending servers
Greylisting typically tracks the combination of sender IP, recipient, and sender domain. But some large email providers send retries from a different IP address than the original attempt, especially when they use multiple outbound servers behind a load balancer. If the retry comes from a different IP, your greylisting system may treat it as a brand new, unrecognized attempt and reject it again. This can create a loop where legitimate mail never quite gets through.
Non-standard mail software
Not every sending system follows the retry convention properly. Some marketing platforms, internal notification tools, and older mail servers don't retry at all after a soft rejection. If a sender's software doesn't understand a 4xx temporary error the way it's supposed to, greylisting will silently swallow their mail.
How to Use Greylisting Without Losing Legitimate Mail
Most modern implementations aren't as blunt as they used to be. A few practical adjustments make a big difference:
- Whitelist known-good senders. Once a domain has proven itself, skip the greylisting delay entirely for future messages.
- Shorten the retry window for trusted domains. You don't need a 15-minute delay for senders with strong sender reputation and clean sending history.
- Combine it with other spam prevention techniques. Greylisting shouldn't be your only defense. Pair it with SPF, DKIM, DMARC, and content filtering so you're not relying on a single method.
- Monitor complaints about missing email. If customers report delays around account signups or password resets, check whether greylisting is the culprit before assuming it's a bug elsewhere.
We wrote more about the mechanics of this kind of filtering in how content filters evaluate your emails, which covers what happens after a message clears the greylisting stage.
Is Greylisting Still Worth Using in 2024?
For smaller mail servers without a dedicated spam-fighting budget, yes. It's still one of the most cost-effective ways to cut spam volume without expensive filtering software. Larger operations with mature reputation-based filtering sometimes phase it out because the delay-to-benefit ratio drops once you already have strong content and reputation filters in place.
If you're managing email on a VPS yourself, greylisting is usually configured at the mail transfer agent level (Postfix, Exim, and similar). Getting the retry window and whitelist rules right takes some testing. A managed setup handles this kind of tuning for you, so you get the spam reduction without the awkward side effects of an overly aggressive configuration. If you want to see how this fits into a broader mail setup, our email hosting overview covers the pieces that work together to keep your inbox both clean and reliable.
The Takeaway
Greylisting is a clever, low-cost way to filter out a big share of spam before it ever reaches deeper analysis. The tradeoff is delivery delay, which mostly only affects senders whose mail servers behave unusually. For everyday business email, that tradeoff is almost always worth it, as long as you whitelist trusted senders and keep an eye on time-sensitive messages like account verification emails.