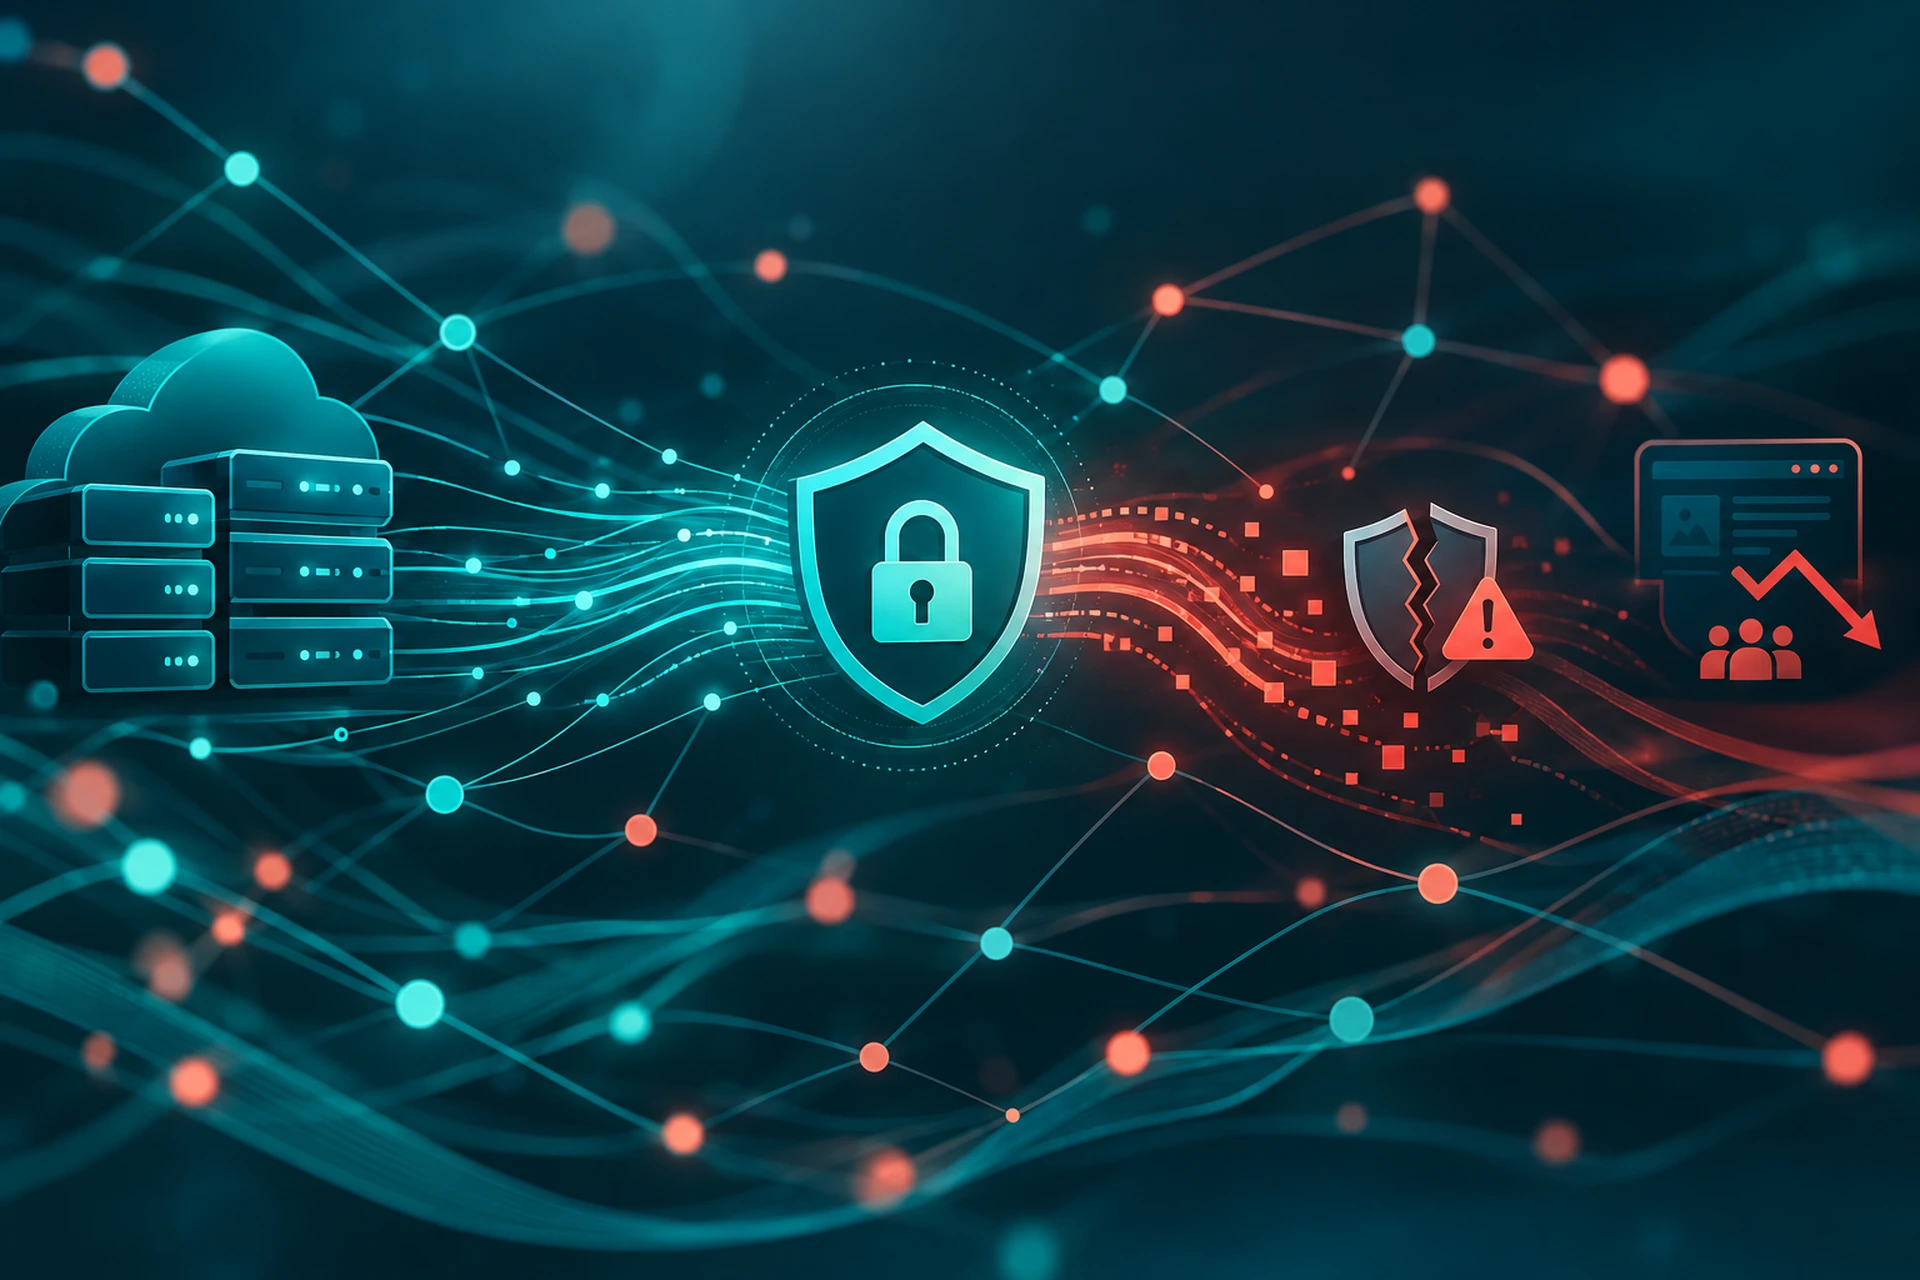
One day your site is running fine. The next morning, visitors see a big red warning screen instead of your homepage. Nothing changed in your code. Nothing changed in your design. Your SSL certificate just expired, and nobody caught it in time.
This happens more often than most site owners realize, and the fallout is bigger than a scary browser message. Expired certificates quietly chip away at traffic, rankings, and customer trust, often before anyone on your team even notices.
Why SSL Certificates Expire in the First Place
SSL certificates aren't permanent. They're issued with a set lifespan, and that lifespan has gotten shorter over the years. Certificates used to last up to three years. Then it dropped to two. Now most certificates, including free ones from Let's Encrypt, are valid for just 90 days.
Shorter lifespans are actually good for security. They limit how long a compromised key stays useful, and they push the industry toward automation. But they also mean renewal has to happen roughly four times a year instead of once every few years. That's four more chances for something to slip through the cracks.
Common Reasons Renewals Get Missed
- The person who set up the certificate left the company, and nobody inherited the responsibility.
- An expired payment method silently blocked an auto-renewal charge.
- A DNS change broke the domain validation the certificate authority needed to confirm ownership.
- A manual renewal reminder got buried in an inbox full of other notifications.
- A server migration moved the site without moving the certificate renewal process along with it.
None of these causes are dramatic. That's exactly the problem. Renewal failures rarely come from a big obvious mistake. They come from small gaps in a process nobody was really watching.
What Actually Happens When a Certificate Expires
Every major browser treats an expired certificate as a serious warning, not a minor notice. Chrome, Firefox, and Safari all show a full-page interstitial telling visitors the connection isn't private. There's no small icon change or subtle padlock difference. It's a wall between your visitor and your content.
Most people don't click through that wall. Studies on browser warning behavior consistently show that a large majority of visitors simply leave instead of risking a connection flagged as unsafe. If you're running an ecommerce store, that's checkout abandonment at scale. If you're running a SaaS product, that's locked-out users and a flood of support tickets within minutes.
The SEO Damage You Don't See Immediately
Search engines treat HTTPS as a baseline requirement, not a bonus. When Googlebot crawls a site with an expired certificate, it can't reliably verify the connection, and indexing can stall. If the outage lasts more than a few hours, you may see temporary ranking drops or delayed re-indexing once the certificate is fixed.
The frustrating part is that the SEO hit can outlast the actual outage. Rankings don't always snap back the moment your certificate is valid again. Recovery can take days, especially if the expiration coincided with a Google crawl of your most important pages.
Why "Set It and Forget It" Isn't Actually Set and Forget
A lot of site owners assume that once they install an SSL certificate, they're done. Technically, automated renewal tools like ACME and Let's Encrypt's certbot were built to make this true. In practice, automation fails silently all the time.
A renewal script can fail because of a permissions change, a firewall rule update, or a cron job that stopped running after a server reboot. If nobody is actively monitoring certificate expiration dates separately from the renewal process itself, the first sign of trouble is often the outage itself.
This is one of the reasons why SSL certificate hosting that includes active monitoring matters so much more than it sounds like it should. The certificate needs to renew, and someone or something needs to verify that it actually did, independent of the automation that's supposed to handle it.
What Good SSL Certificate Hosting Actually Looks Like
Reliable SSL certificate hosting isn't just about installing a certificate once and walking away. It involves tracking expiration dates proactively, retrying failed renewals automatically, and alerting someone when a renewal attempt doesn't go through cleanly. On a managed server, that's exactly what should be happening in the background. We handle certificate renewal and monitoring as part of every managed plan, so an expired cert simply isn't something our customers have to think about.
If you're managing your own server, this is worth building into your monitoring stack specifically. Don't just monitor uptime. Monitor certificate expiration as a separate metric, ideally with an alert that fires 14 and 7 days before expiration, not the day of.
How to Catch Renewal Problems Before Visitors Do
A few habits go a long way here:
- Set calendar reminders or automated alerts tied to your certificate's actual expiration date, not just the renewal schedule.
- Test your renewal automation periodically instead of assuming it's still working.
- Keep payment methods for any paid certificates current, and make sure billing failures trigger a notification to a real person.
- Use uptime monitoring that checks for valid HTTPS responses, not just a basic ping.
- Document who owns certificate renewal on your team, so it doesn't depend on one person's memory.
We've also written about the broader question of why SSL certificate hosting matters more than just showing a padlock in the browser, which covers the trust side of this in more depth. And if you're still deciding between certificate types, our comparison of DV, OV, and EV certificates is a good next read.
The Real Cost Adds Up Quietly
A single missed renewal might only last a few hours before someone notices and fixes it. But the compounding damage is real: lost sales during the outage, a dip in search visibility that takes days to recover, and a chunk of visitors who saw the warning screen and simply never came back to check if it was fixed.
None of this requires a sophisticated attack or a major server failure. It just requires one quiet gap in a renewal process that everyone assumed was handled. That's the real danger of SSL renewal failures. They're boring, they're preventable, and they still cost businesses real money every single day.
The fix isn't complicated. It just requires treating certificate renewal as an ongoing responsibility instead of a one-time setup task, whether that means building solid monitoring yourself or choosing a host that already treats it that way.