If you send email from one domain, DKIM SPF DMARC setup is already fiddly. Now imagine managing it across five domains, or a parent domain plus a handful of subdomains for marketing, transactional mail, and support tickets. Things get messy fast, and a single misconfigured record can tank deliverability for an entire brand.
This happens to growing companies all the time. You start with one domain sending invoices. Then marketing spins up a campaign domain. Then a SaaS product adds a subdomain for transactional email through a third-party service. Before long, nobody remembers which SPF record lives where, or whether DMARC is even enforcing anything.
Why DKIM SPF DMARC Setup Gets Complicated With Multiple Domains
Each domain and subdomain needs its own attention when it comes to email authentication. DNS records don't automatically cascade the way some people assume. A DMARC record on your root domain does not automatically protect a subdomain unless you plan for it. An SPF record you set up for your main domain won't help your marketing subdomain send mail that passes authentication.
On top of that, every sending source, your CRM, your email marketing tool, your transactional email provider, your internal mail server, needs to be accounted for. Miss one, and that service's mail either fails authentication or gets flagged as spoofed.
The Subdomain Inheritance Problem
DMARC has a subdomain policy option (sp=) that lets you set a different enforcement level for subdomains than for your root domain. This matters a lot when you have domains you don't actively send from. Those "parking" domains and subdomains should get a strict reject policy, because legitimate mail should never come from them. Active sending subdomains need their own SPF and DKIM configuration, plus a DMARC policy that matches your risk tolerance.
A common mistake is assuming that once the root domain has DMARC in place, everything underneath it is covered. It's not, unless you explicitly set sp=reject or a matching policy. Without that, attackers can register lookalike subdomains or spoof unused ones, and your main DMARC record won't stop them.
Mapping Out Every Sending Source First
Before touching a single DNS record, make a list. Write down every domain and subdomain you own, and every service that sends mail on your behalf for each one. This includes obvious things like your email provider, but also often-forgotten sources: your CRM, your helpdesk software, invoicing tools, and any marketing automation platform.
For each sending source, you'll need its specific SPF include mechanism or IP range, and in most cases, a DKIM selector it provides. Skipping this step is the number one reason multi-domain DKIM SPF DMARC setup goes wrong. People configure the obvious sender and forget the other three tools quietly sending mail in the background.
One SPF Record Per Domain, Not Per Service
A frequent error is trying to add a separate SPF record for each sending service. DNS only allows one SPF record per domain. If you have multiple senders, you combine them into a single record using multiple include mechanisms, like this:
v=spf1 include:_spf.google.com include:sendgrid.net include:mailgun.org ~all
Also keep an eye on the 10 DNS lookup limit SPF enforces. Each include can trigger additional lookups, and once you pass ten, mail servers may treat the whole record as a permanent error, which breaks authentication entirely across every domain using it.
DKIM Selectors Need to Stay Unique
DKIM works differently from SPF. Instead of one record, you publish a separate DKIM record for each sending service, identified by a unique selector. If your transactional provider uses selector s1 and your marketing tool also tries to use s1, you'll get a conflict. Always use the selector each provider assigns you, and keep a running list of which selector belongs to which service and domain. This list becomes invaluable when you're troubleshooting six months later and can't remember what's active.
Rolling Out DMARC Gradually Across Domains
When you're managing authentication across multiple domains, resist the urge to jump straight to a reject policy everywhere. Start every domain at p=none with reporting turned on. This gives you visibility into what's actually sending mail as each domain before you start blocking anything.
Review the aggregate reports for a few weeks. You'll often find surprises, an old marketing tool nobody uses anymore, a forgotten internal script sending notification emails. Fix or remove those sources, then move each domain to quarantine, and eventually reject, once you're confident everything legitimate is passing.
Do this domain by domain rather than all at once. A problem on one domain shouldn't force you to delay progress everywhere else.
Centralizing DNS Management Saves You Later
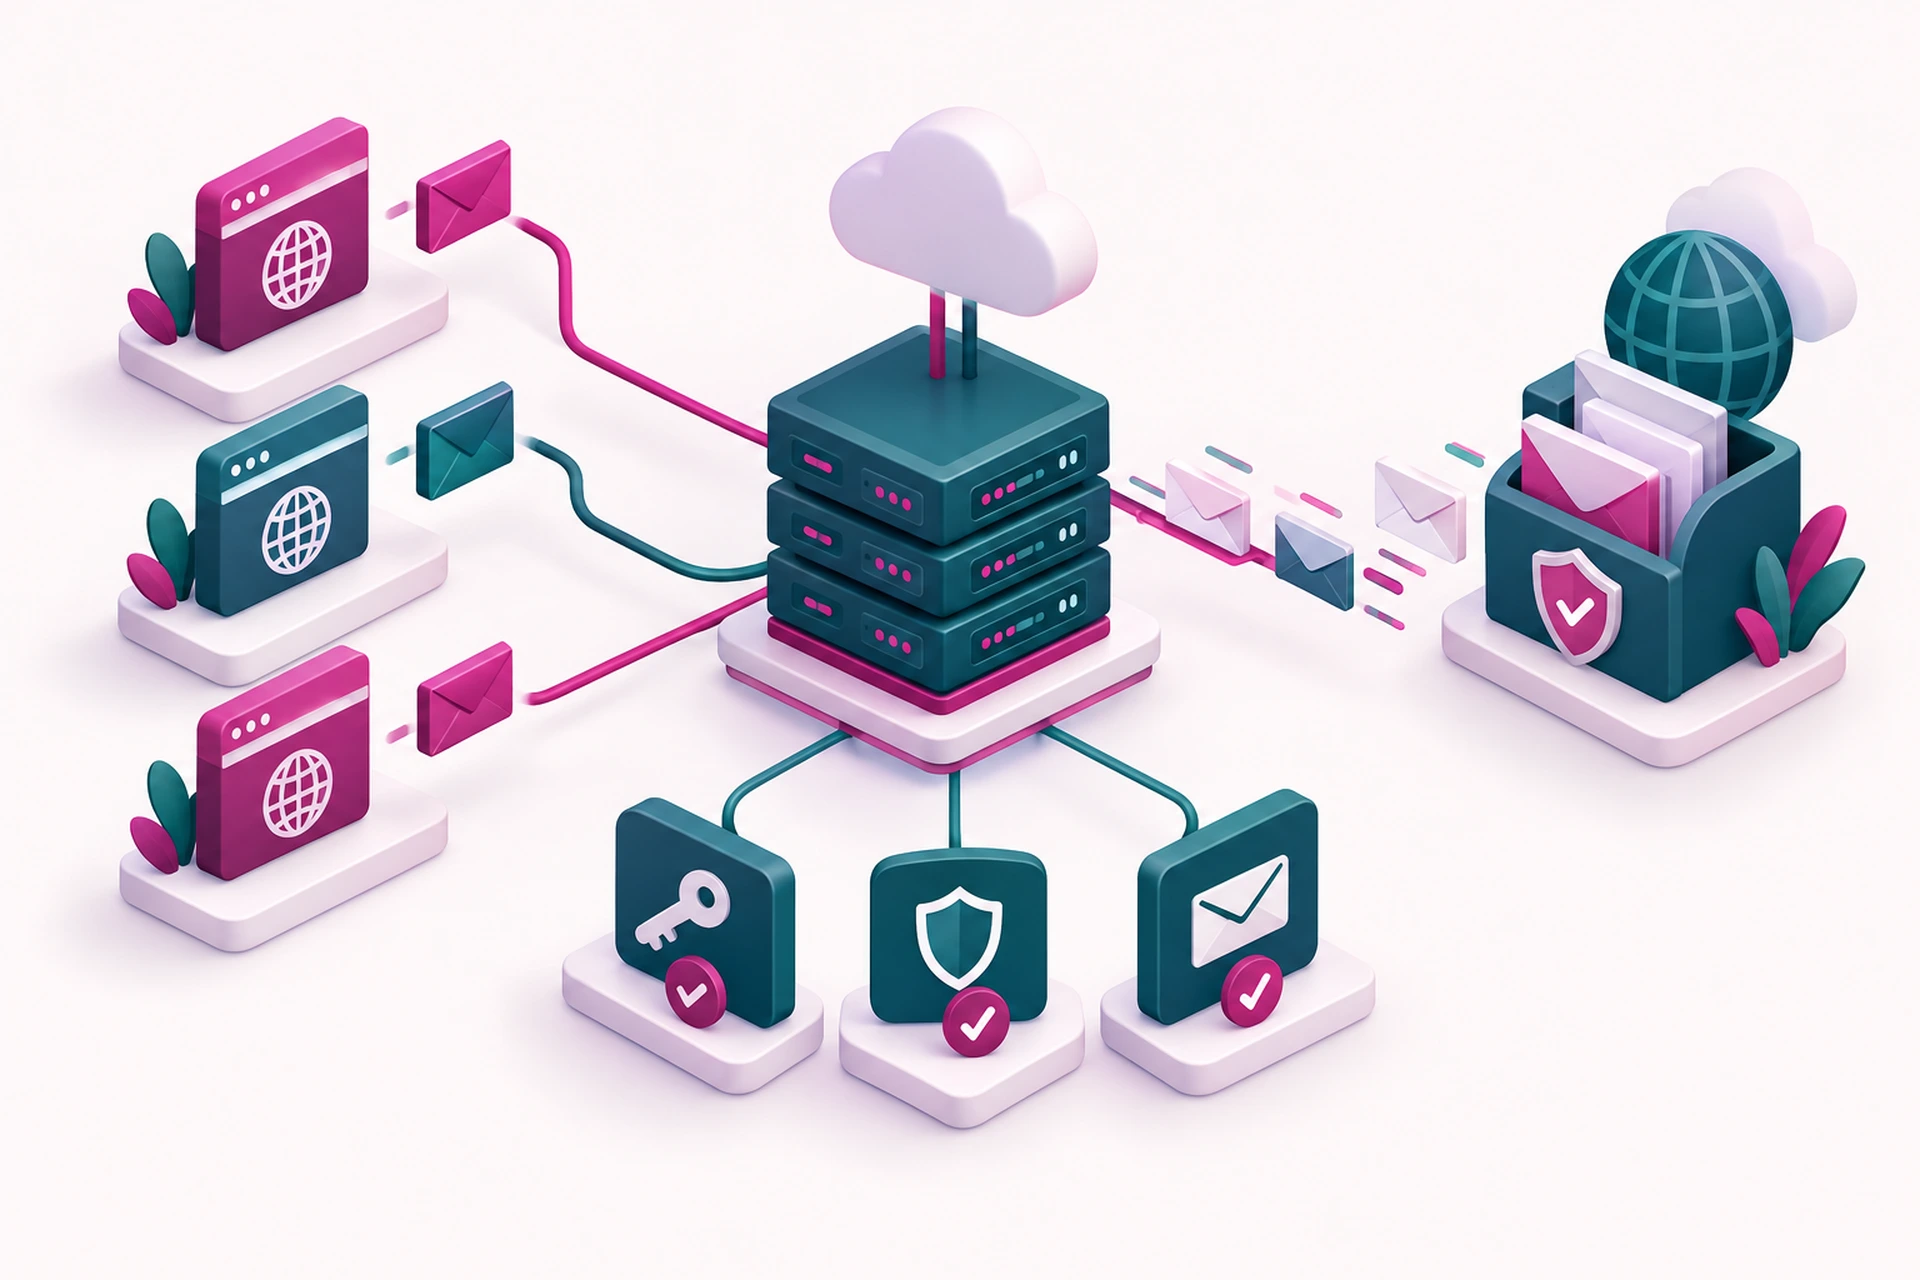
The biggest practical challenge with multi-domain DKIM SPF DMARC setup isn't the theory, it's keeping track of records across different registrars and hosting panels. If your domains are scattered across providers, managing this consistently becomes a real headache. Keeping DNS for all your domains in one place, even if the domains themselves are registered elsewhere, makes it much easier to audit records, spot gaps, and update things when a sending service changes its requirements. We handle DNS management for clients this way specifically because scattered DNS control is where most multi-domain mistakes happen.
We've covered the fundamentals of getting these records right in A Plain-Language Guide to Setting Up DKIM, SPF, and DMARC for Your Domain, and if you want to understand what each DMARC enforcement level actually does, DMARC Policies Explained walks through the differences. If you're unsure whether your current setup is working at all, How to Check Whether Your DKIM SPF DMARC Setup Is Actually Working Correctly is a good next stop.
A Simple Framework to Keep Things Organized
For each domain and subdomain you own, keep a record of four things: who sends mail from it, what SPF includes are needed, what DKIM selectors are active, and what DMARC policy level it's currently at. Revisit this list quarterly, especially after adding any new marketing tool or SaaS integration that sends email.
Multi-domain email authentication isn't harder because the technology changes. It's harder because it requires ongoing bookkeeping. Treat it that way, and the mess sorts itself out.